🛡️ Stop card-testing attacks (WooCommerce)
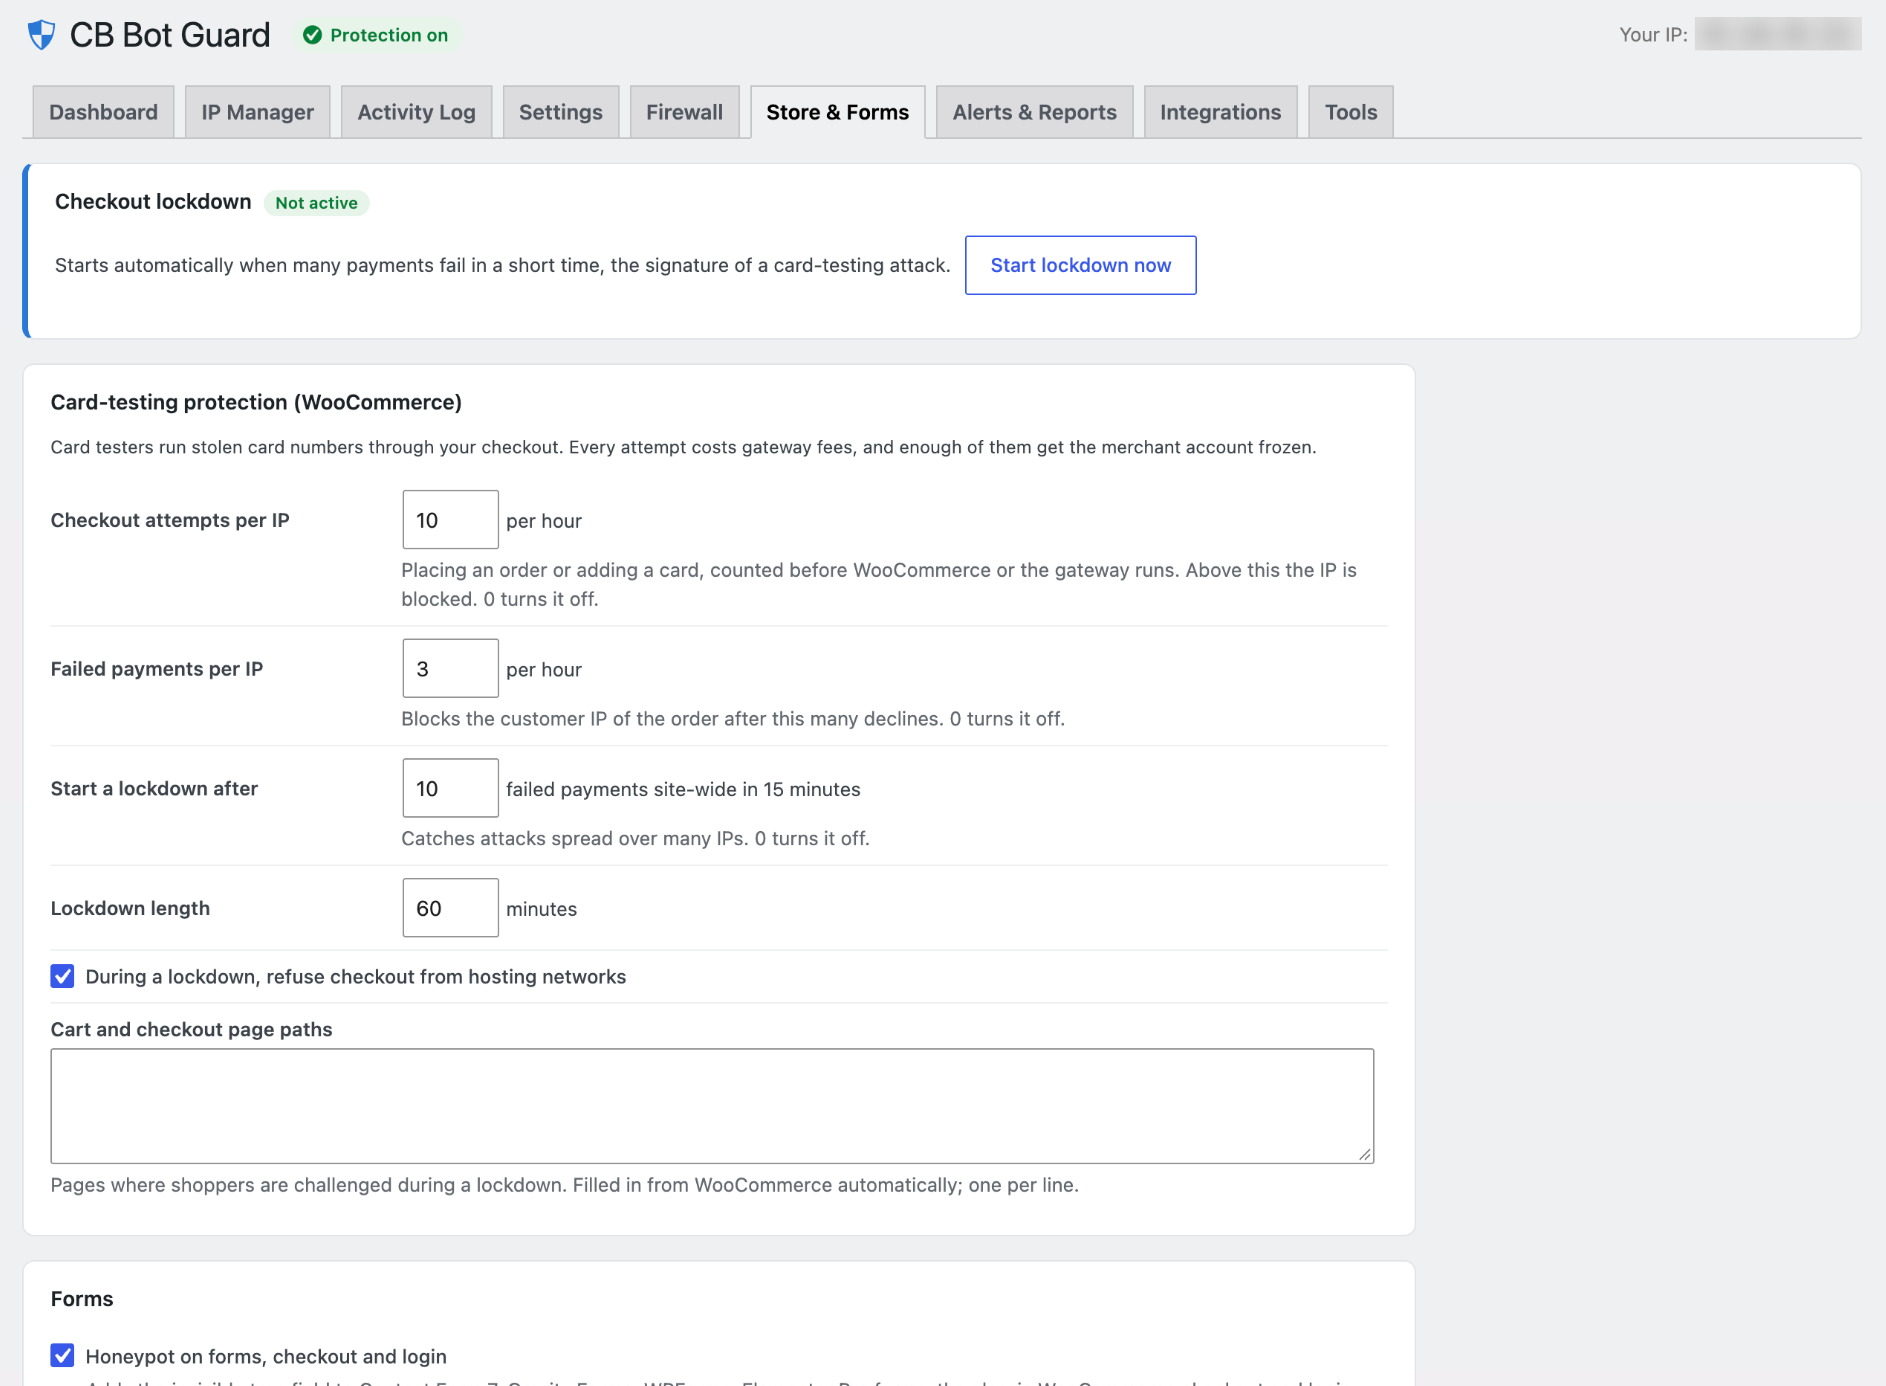
- Checkout attempt limit: stops bots that hammer your checkout, before WooCommerce or your payment gateway does any work.
- Failed payment limit: automatically blocks visitors who rack up declined cards.
- Automatic checkout lockdown: when payments start failing across your store, shoppers pass a quick browser check before paying and bot networks can’t check out at all. It ends by itself when the attack is over.
- Cut gateway fees and protect your merchant account from the chargebacks and freezes that card testing causes.
🌍 Smarter firewall rules
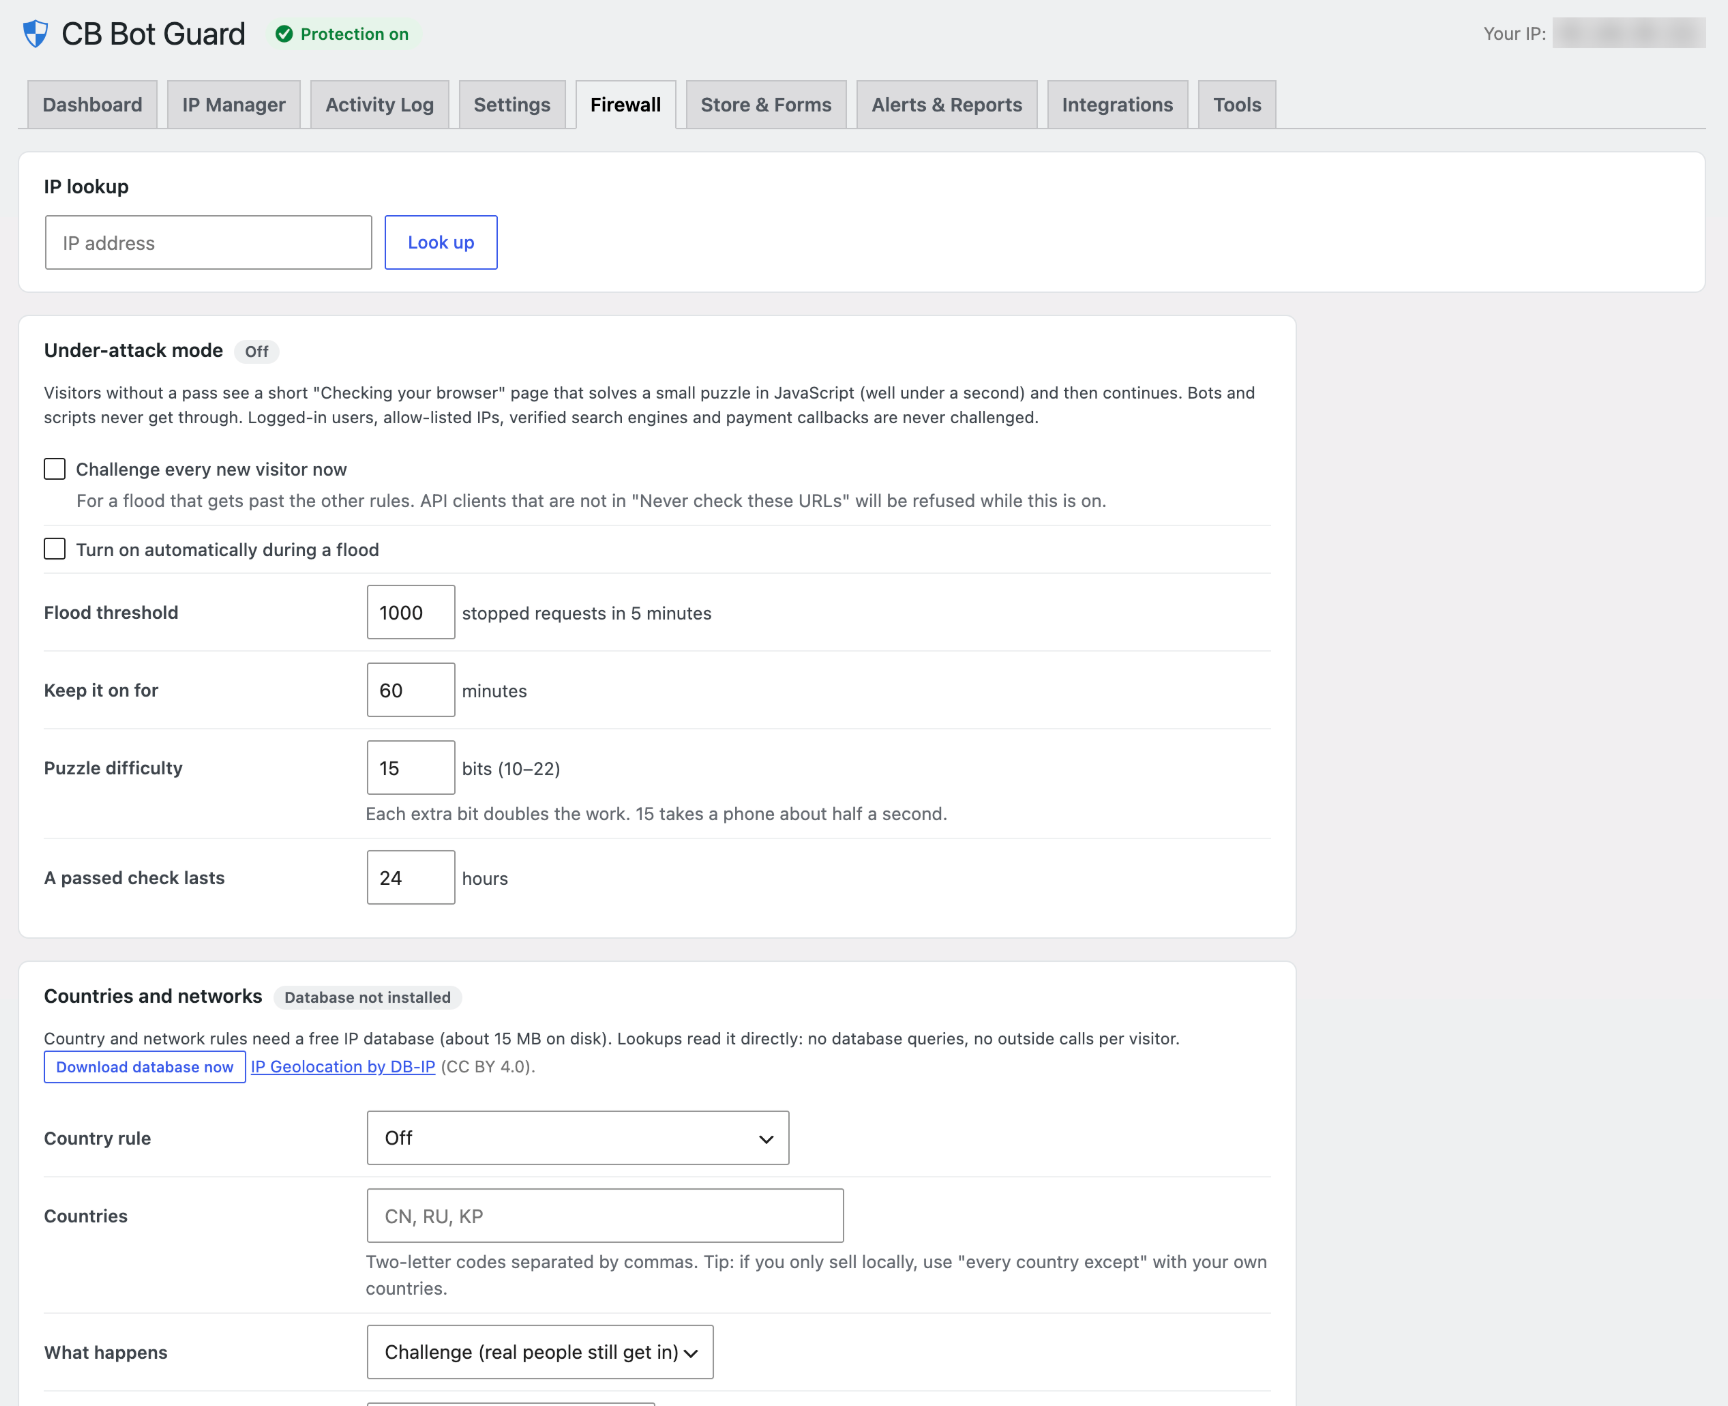
- Browser challenge: a middle ground between allowing and blocking. Real visitors pass a check that takes under a second and isn’t asked again for a day. Bots never get through. No third-party service, and no puzzles for your customers to solve.
- Under-attack mode: challenge every new visitor during a flood, with one click or automatically.
- Country rules: challenge or block chosen countries, or allow only the countries you sell to.
- Hosting network blocking: most scrapers and attack tools run on cloud servers (AWS, DigitalOcean, Hetzner, OVH and 50+ more), where real shoppers almost never browse from. Challenge or block them in one setting.
- Block any network by its ASN number.
- IP reputation lists: Spamhaus DROP, Tor exit nodes and FireHOL, updated daily.
- AbuseIPDB integration: instantly block attackers that are already known, and report yours back.
- AI crawler opt-out: tell AI training bots to stay out through robots.txt.
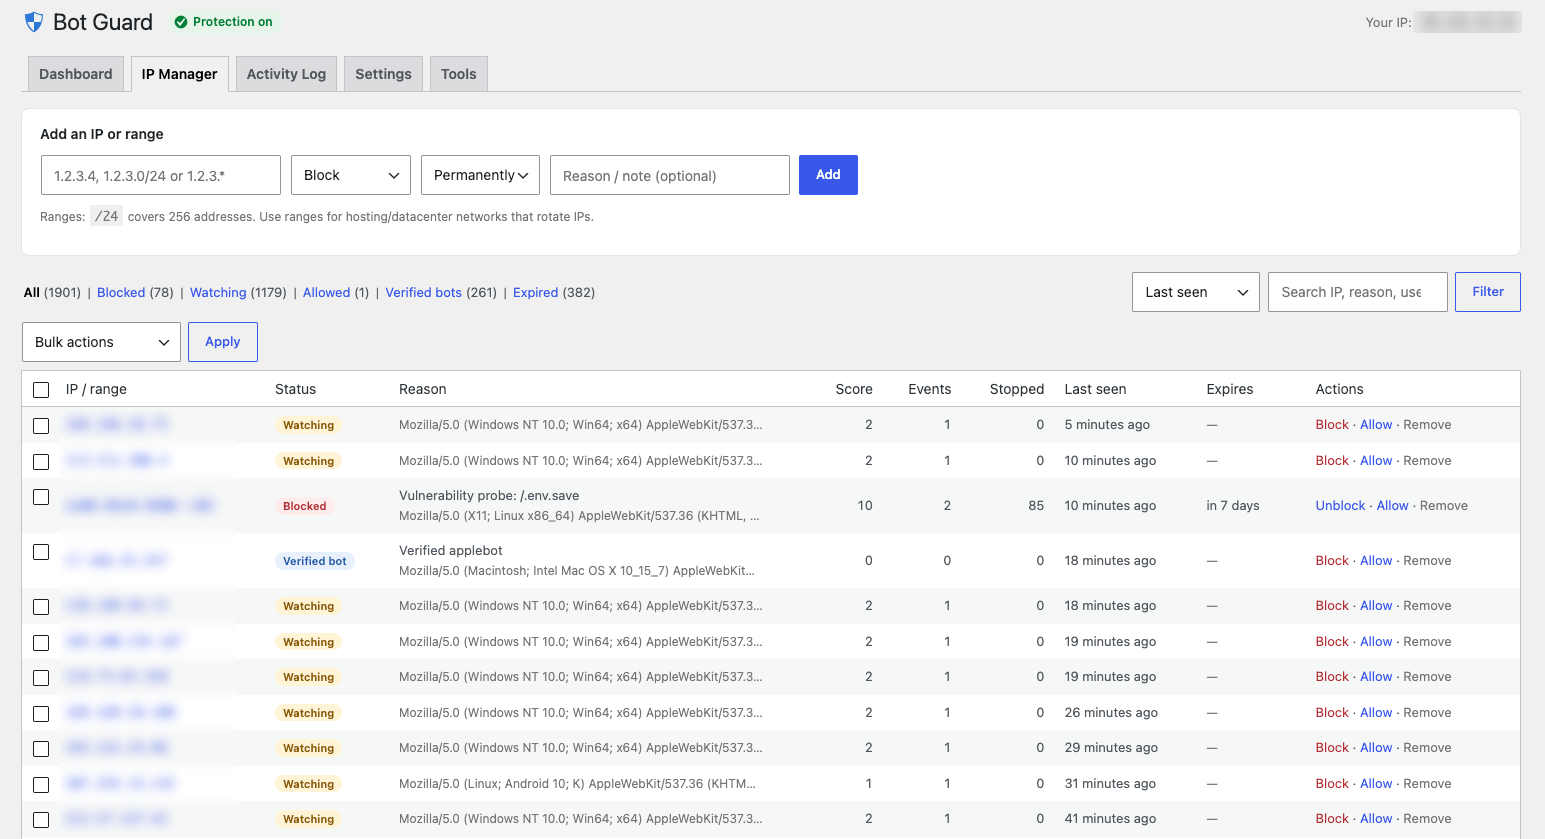
- IP lookup: see the country, network and reputation of any visitor.
📝 Spam-proof forms and logins
- Honeypot traps for Contact Form 7, Gravity Forms, WPForms, Elementor Pro forms, WooCommerce checkout and login forms.
- “Too fast” detection: rejects forms submitted faster than a human could fill them in.
- Disposable email blocking: stops throwaway addresses at registration and checkout, using a community list updated weekly.
- Per-account login limit: stops slow brute-force attacks spread across many IPs, without ever locking out the real owner on their usual devices.
- Banned usernames: instantly blocks anyone trying “admin”, “root” or “test” when no such user exists.
🔔 Alerts and reports
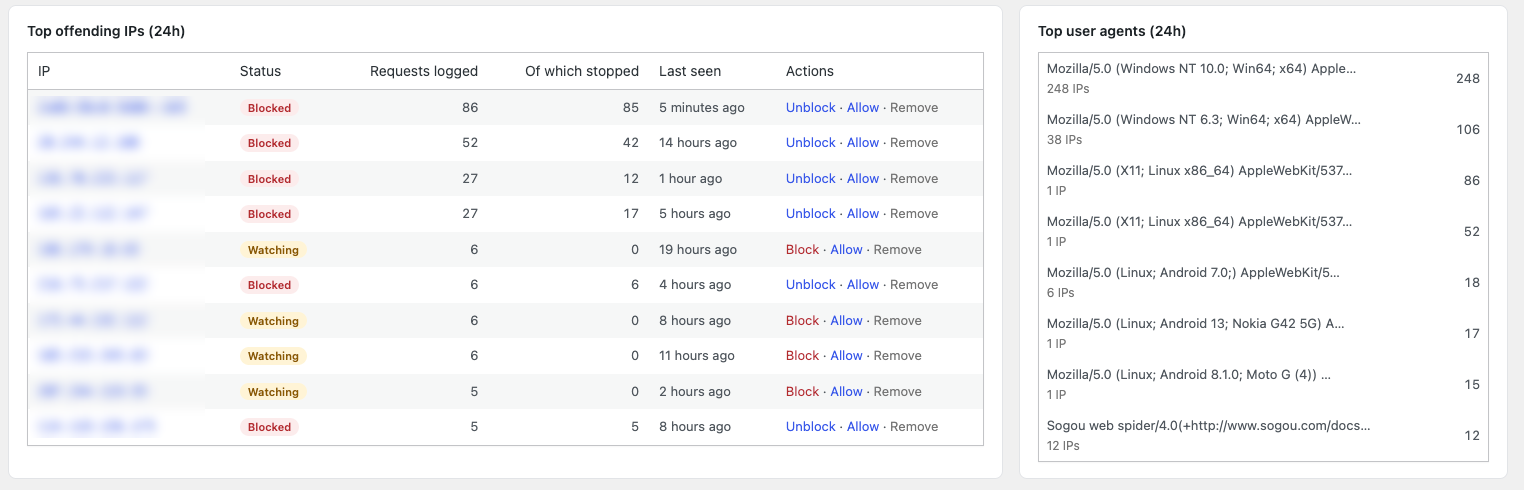
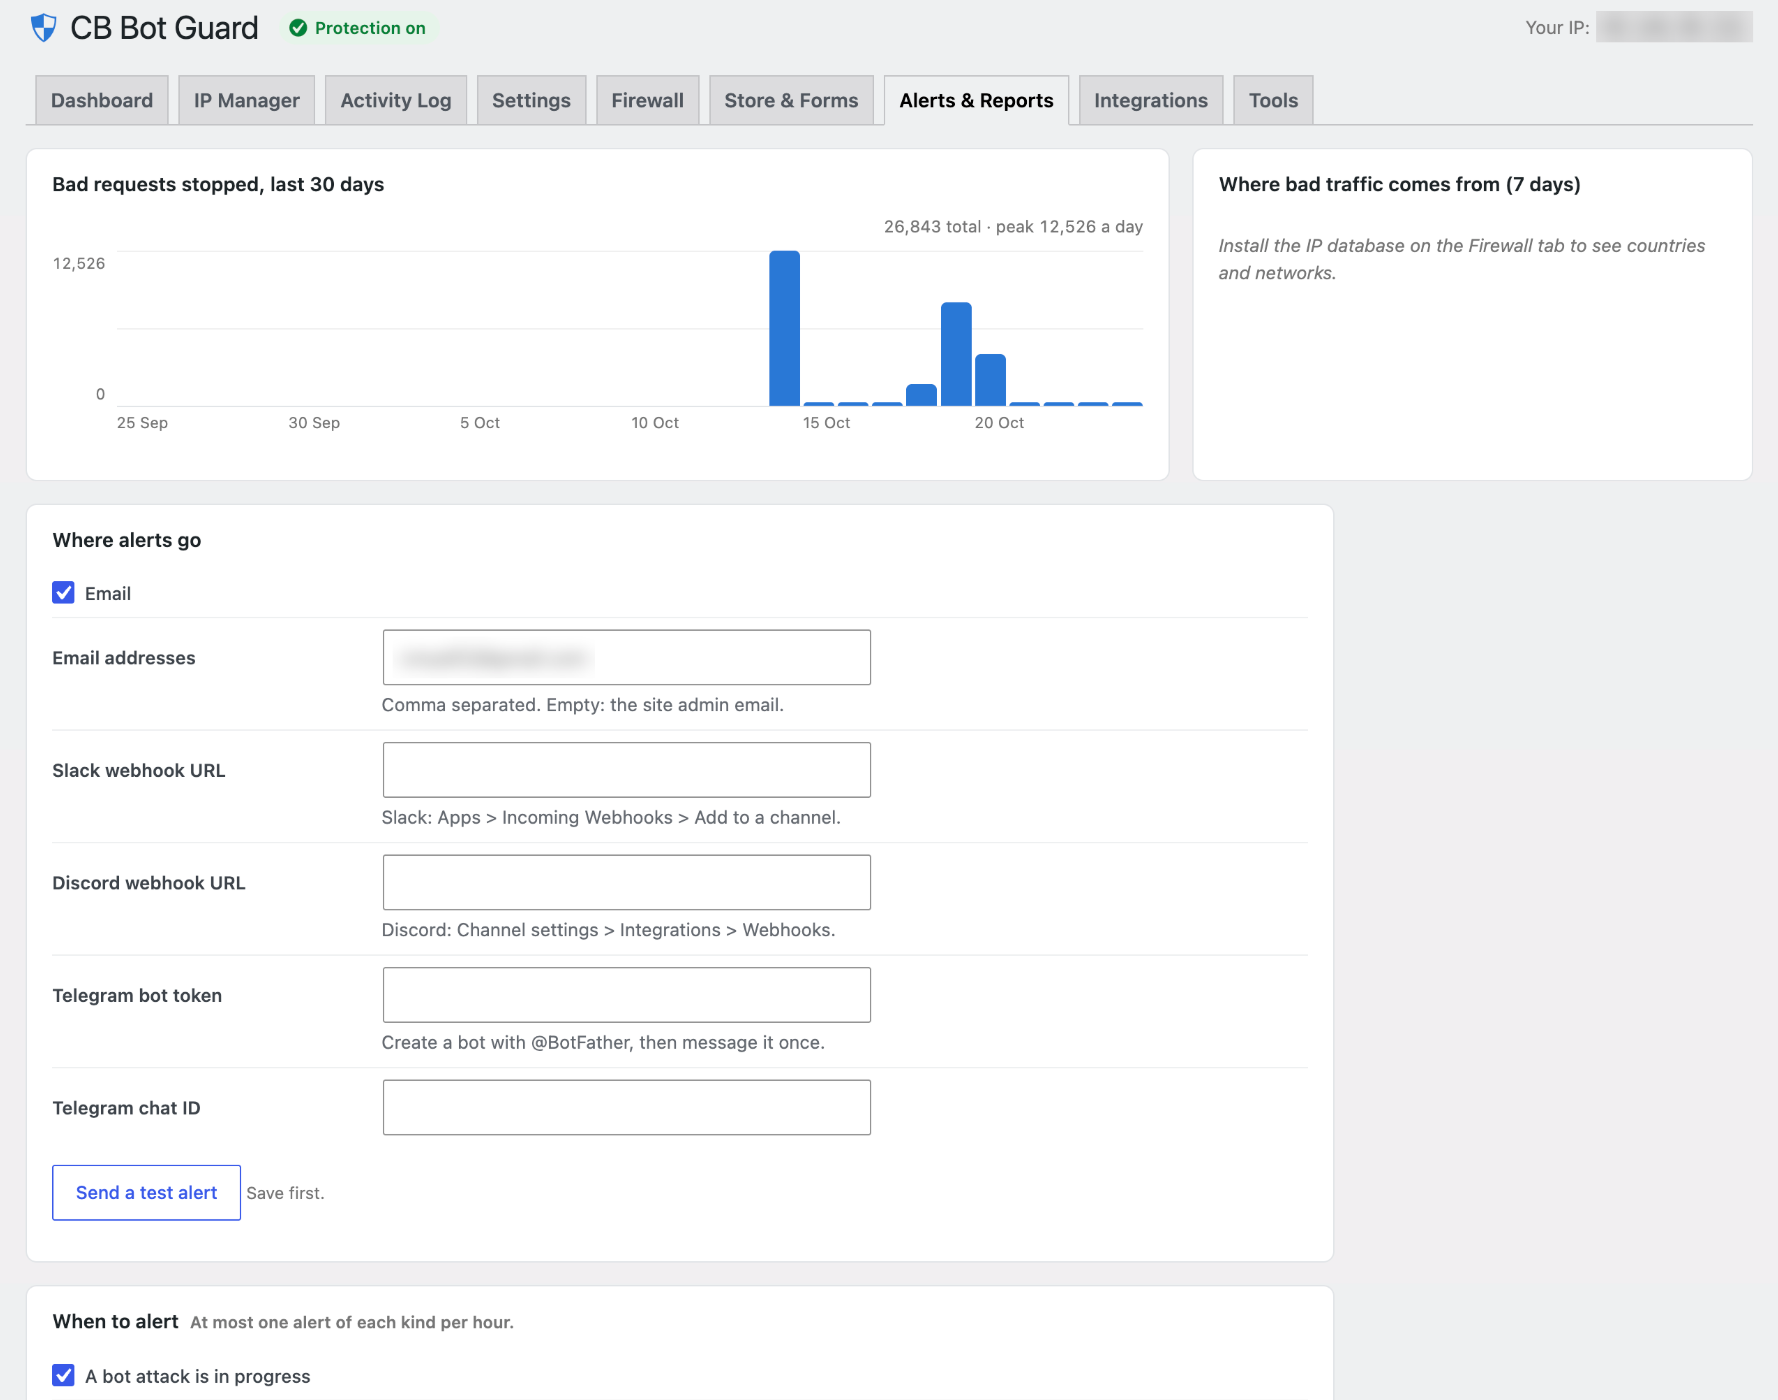
- Real-time attack alerts by email, Slack, Discord or Telegram, with the top offending IPs.
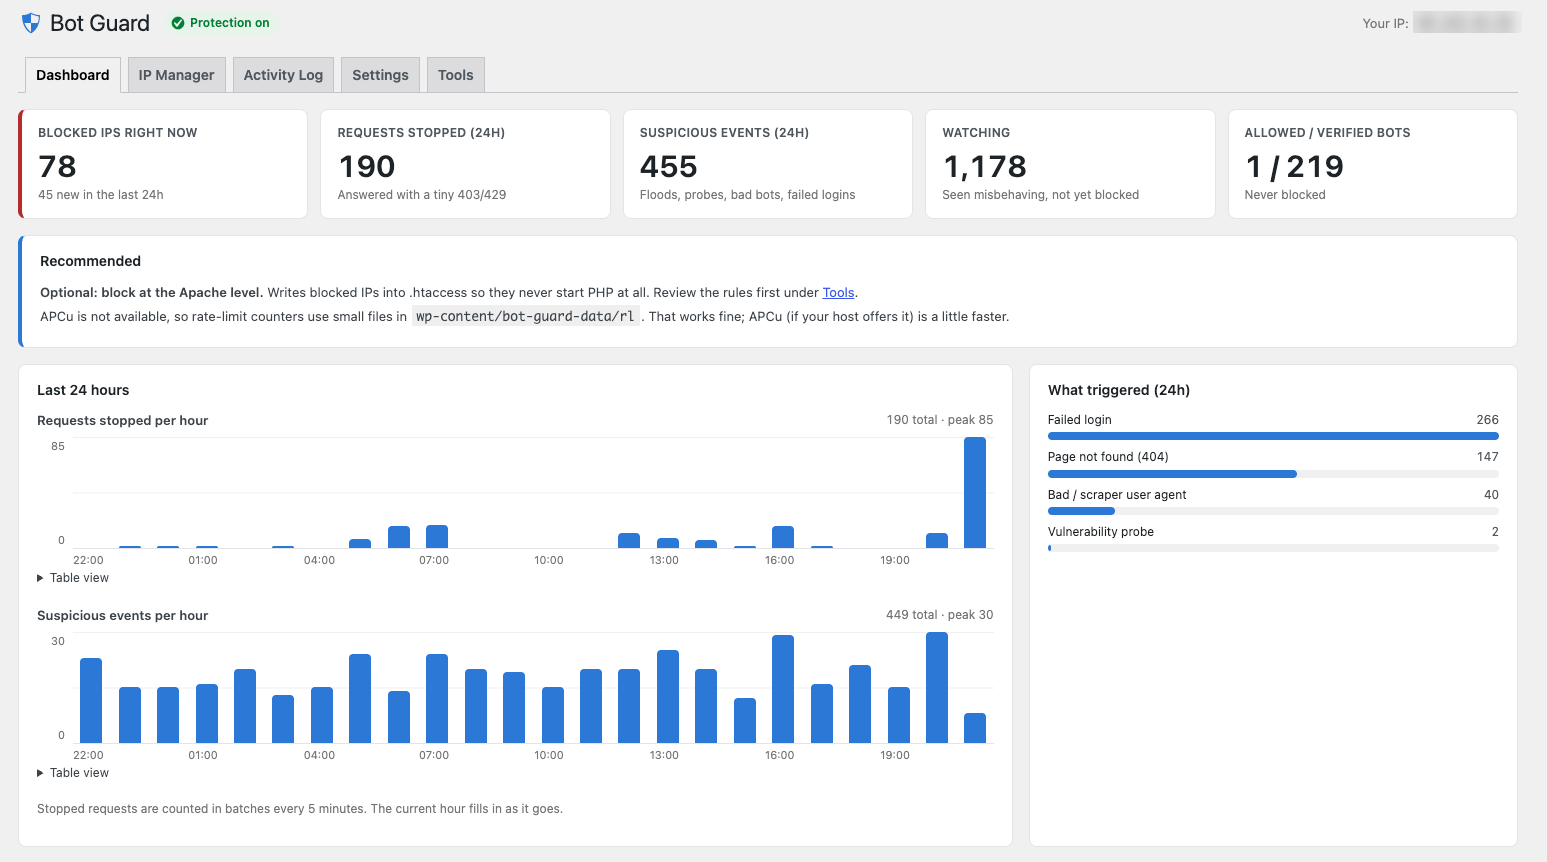
- Weekly security report by email: requests stopped, server time saved, threats detected, top countries and offenders, and the change from last week.
- White-label reports: your agency or client name on every report.
- 30-day dashboard chart showing where bad traffic comes from, by country and network.
🔗 Integrations for agencies and busy sites
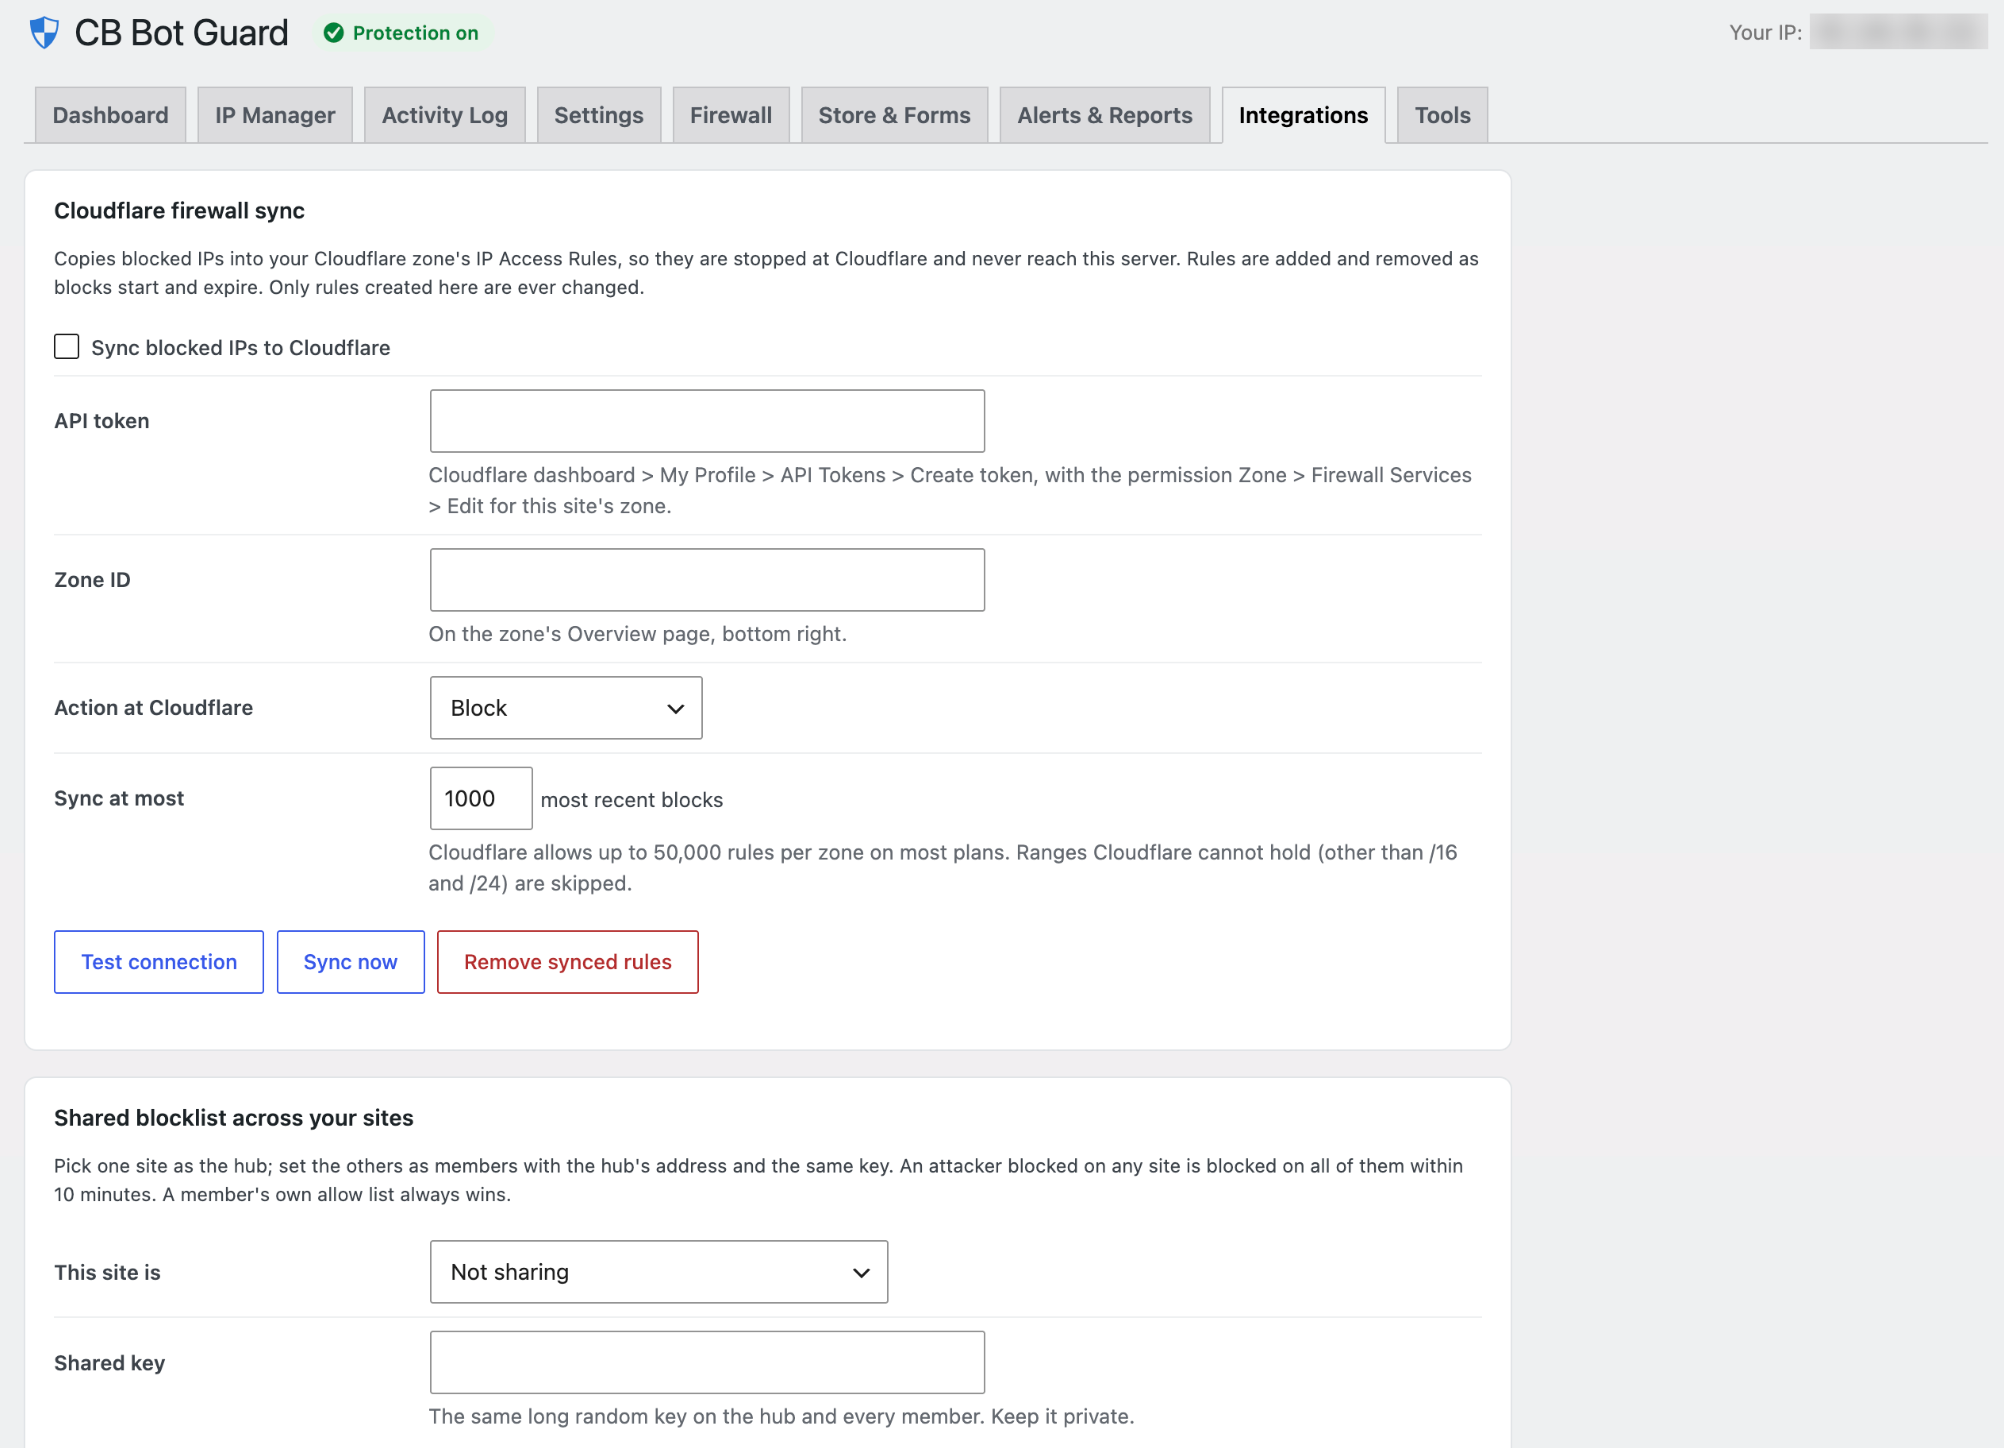
- Cloudflare firewall sync: blocked IPs are pushed to Cloudflare automatically and stopped before they reach your server.
- Shared blocklist across sites: block an attacker on one site and it’s blocked on all your sites within minutes. Private and secure between your own sites, with no outside service.
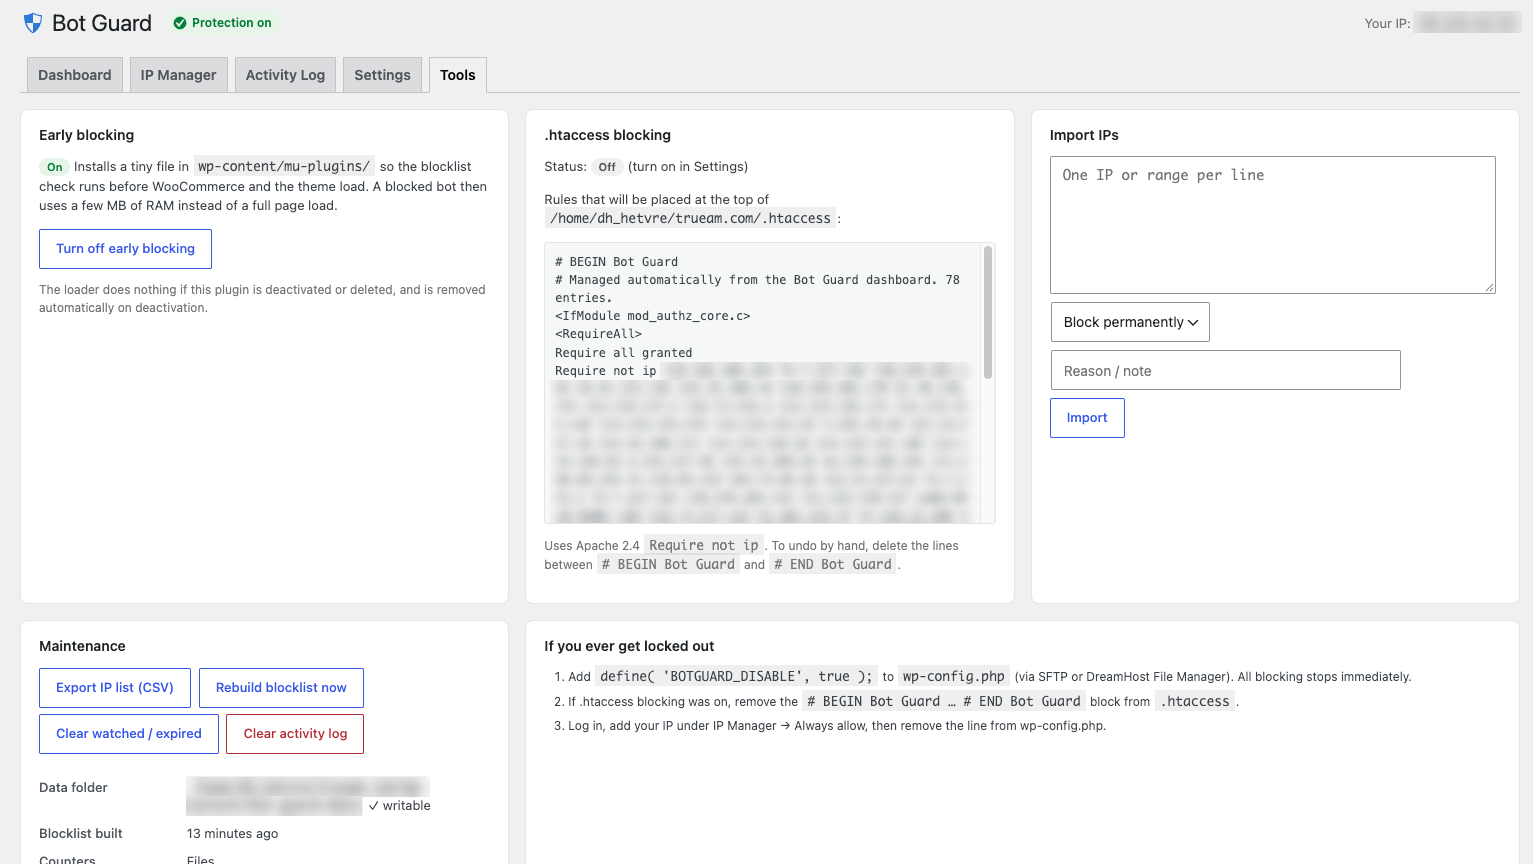
- Nginx support: a ready-to-include deny file, the Nginx counterpart of the free plugin’s .htaccess blocking.
⚡ Still lightweight
- No database queries for normal visitors.
- Pro rules run before your theme and plugins load.
- Logged-in users, allow-listed IPs, Google/Bing and payment gateway callbacks are never affected.
Reviews
There are no reviews yet.